 Peplink Gold Partner
Status of the German implementation
Directive (EU) 2022/2555 (NIS2) is transposed into German law by the NIS-2 Implementation and Cybersecurity Strengthening Act (NIS2UmsuCG), published on 5 December 2025 (BGBl. 2025 I No. 301) and in force since 6 December 2025 with no transition period.
Its core is the revised BSI Act (BSIG) with two categories: particularly important and important entities.
Status as of 22 September 2026. This is a technical summary, not legal advice. For classification, use the BSI self-assessment tool.
- NIS2UmsuCG in force: 6 December 2025
- Statutory registration deadline (§ 33 BSIG): 6 March 2026 – expired
- BSI tolerance period for late registrations: 31 July 2026 – expired
- Register in the BSI portal now
Deadlines and key facts
Source: BSIG and BSI. Status: 22 September 2026.
| In force since | 6 December 2025 – no transition period |
|---|---|
| Entities in scope | approx. 29,500 (previously around 4,500 KRITIS operators), BSI figure |
| Registration (§ 33 BSIG) | within 3 months of falling into scope; existing cases: 6 March 2026 |
| Incident reporting (§ 32 BSIG) | early warning 24 h, notification 72 h, final report 1 month |
| Fines (§ 65 BSIG) | up to EUR 10 million or 2 % of worldwide total turnover; important entities up to EUR 7 million or 1.4 % |
Who is affected?
Two questions decide: does your activity match an entity type in Annex 1 or 2 of the BSIG, and do you exceed the size thresholds?
- Important entities (§ 28 (2)): at least 50 employees or more than EUR 10 million turnover and more than EUR 10 million balance sheet total.
- Particularly important entities (§ 28 (1)): at least 250 employees or more than EUR 50 million turnover and more than EUR 43 million balance sheet total, in an Annex 1 entity type. Operators of critical installations count regardless of size.
Headcounts follow EU SME Recommendation 2003/361/EC. Managed services providers are in Annex 1 too.
Sectors relevant to our customers
Excerpt from Annex 1 and 2 BSIG.

Energy
Electricity, gas, district heating, fuels, hydrogen. Utilities and grid operators often exceed the 50-employee threshold.

Shipping and ports
Passenger and freight carriers in inland, sea and coastal shipping, managing bodies of ports, operators of port installations – all in Annex 1.

Supply chain
Even out of scope yourself, NIS2 reaches you through customers: § 30 (2) no. 4 requires supply chain security, and requirements get passed on.
Duties under the BSIG

Registration (§ 33)
Within three months of falling into scope via "Mein Unternehmenskonto" and the BSI portal; changes within two weeks.

Risk management (§ 30)
Appropriate, proportionate, state-of-the-art measures in ten areas.

Incident reporting (§ 32)
Significant incidents: early warning within 24 hours, notification within 72 hours, final report after one month.

Management (§ 38)
Own and monitor implementation, attend training regularly. Culpable failures make management liable to its entity.

Attack detection, evidence (§§ 31, 39)
Operators of critical installations run attack detection and prove implementation every three years.
The ten measure areas under § 30 (2) BSIG
Outcomes, not products, in proportion to risk, size and cost:
- Policies on risk analysis and information security
- Incident handling
- Business continuity: backup, recovery, crisis management
- Supply chain security
- Security in acquisition, development and maintenance, incl. vulnerability handling
- Assessing the effectiveness of measures
- Training and awareness
- Cryptography and encryption
- Personnel security, access control, asset management
- Multi-factor authentication, secured and emergency communication
Roadmap: four steps to NIS2 compliance
Clarity first, then technology.
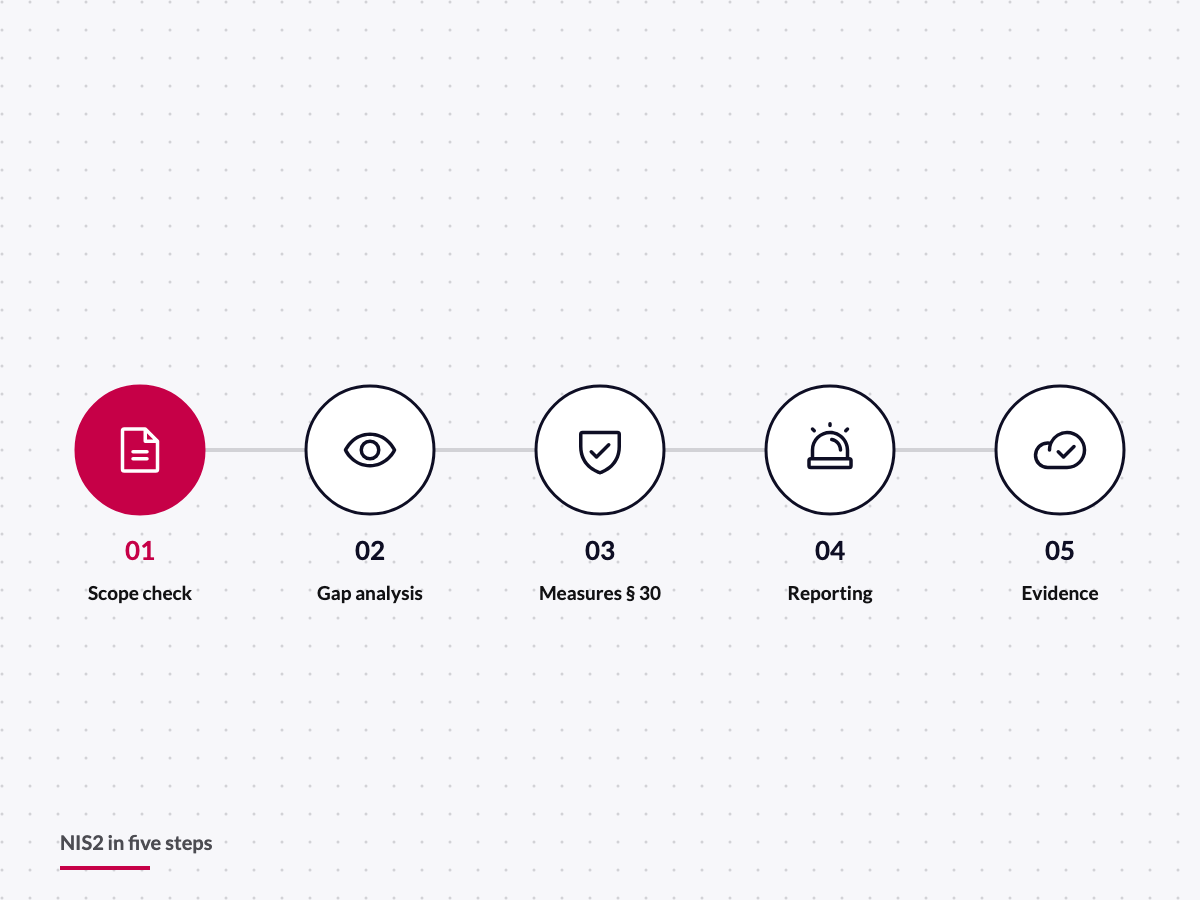
Determine scope and register
Check entity type, headcount, turnover and balance sheet total, document the result, register in the BSI portal.
Inventory and gap analysis
Inventory systems, networks, sites, vessels and remote accesses. Compare with the ten measure areas, prioritise gaps.
Secure network and access
Segment IT and OT, firewalls with clear rule sets, MFA, controlled remote access for manufacturers and contractors.
Detect, report, prove
Monitoring and alerting, a rehearsed 24-hour reporting chain, tested backups, documented measures, trained management.
How DRYNET supports your implementation
We implement § 30 BSIG technically and operate it – onshore, in port, on board. Security: Fortinet (Engage Partner). WAN: Peplink SpeedFusion and our SD-WAN gateway.

Cyber security and firewalls
Firewalls, rule sets, hardening, vulnerability management (§ 30 (2) nos. 1, 5, 8).

Network segmentation
IT, OT, crew and guest networks in zones with controlled transitions (no. 9).

Secure remote access
VPN and zero-trust access with MFA for staff, manufacturers and maintenance companies, logged (nos. 4, 9, 10).

Monitoring and alerting
Networks, links and systems watched around the clock – the basis for § 32 reporting (nos. 2, 6).

Endpoint management
Inventory, patching, encryption and policies for laptops, mobiles and onboard computers (nos. 5, 9).

Compliance and operations
Mapping to BSIG, IMO and IACS UR E26/E27, audit documentation, plus Managed Services and 24/7 Support.
Frequently asked questions about NIS2
Does NIS2 already apply in Germany?
Yes, since 6 December 2025, with no transition period. Registration, risk management and reporting duties apply since then. Status as of 22 September 2026.
The registration deadline has passed. What now?
The statutory deadline ended on 6 March 2026. The BSI tolerated late registrations until 31 July 2026 but did not extend the deadline. Register immediately; failing to register is subject to a fine.
Is a shipping company or a port operator in scope?
Yes, above the size thresholds. Annex 1 lists passenger and freight carriers in inland, sea and coastal shipping, managing bodies of ports and operators of port installations.
What changes for municipal utilities and water suppliers?
Electricity, gas, heat, drinking water and wastewater are in Annex 1. From 50 employees, utilities are important entities. Former KRITIS operators are particularly important and prove their measures every three years.
What deadlines apply when an incident occurs?
Early warning within 24 hours of becoming aware, notification within 72 hours, final report within one month (§ 32 BSIG). Without monitoring and a rehearsed reporting chain, these are hard to meet.
Do I have to buy specific products or certificates?
No. The BSIG prescribes measure areas, not products. ISO 27001 helps with evidence but is not mandatory. What counts: state of the art, proportionality, documentation.
What does the management duty mean in practice?
Management is responsible for implementation, monitors it and attends training regularly (§ 38 BSIG). Tasks can be delegated, responsibility cannot: a named owner, regular reports, documented decisions.
What does NIS2 require from my IT service providers?
Supply chain security (§ 30 (2) no. 4): assess providers, set contractual requirements, control remote access. DRYNET provides documented access paths, logging and fixed contacts.
Request an NIS2 consultation
Prefer to talk? +49 431 55607040
Related pages
Implement NIS2
Let's talk about your scope
Registration, gap analysis, segmentation, monitoring: we tell you what comes first. Call +49 431 55607040 or write to us.