 Peplink Gold Partner
Who counts as critical infrastructure in the German energy sector
In Germany, operators of critical facilities (KRITIS) are defined by the BSI Critical Infrastructure Ordinance (BSI-KritisV). The reference value is 500,000 supplied persons. For the energy sector this translates into thresholds such as these (Annex 1 BSI-KritisV, as of 22 Sept 2026):
- Power generation: 104 MW installed net capacity; black-start plants from 0 MW, primary control reserve from 36 MW
- Transmission and distribution grids: 3,700 GWh of annual energy withdrawn
- Gas production, transmission and distribution: 5,190 GWh per year
- District heating: 2,300 GWh of heat per year or 250,000 connected households
- Below these thresholds NIS2 usually still applies: energy companies with 50 or more employees, or above EUR 10 million in turnover and balance sheet, are generally "important entities"; from 250 employees, or EUR 50 million in turnover and EUR 43 million in balance sheet, they are "essential entities" (as of 22 Sept 2026)
The 2026 legal framework: NIS2 implementation act, BSIG and the KRITIS umbrella act
Germany's NIS2 implementation act entered into force on 6 December 2025 and rewrote the BSI Act (BSIG). Registration with the BSI was due by 6 March 2026; the BSI granted a grace period until 31 July 2026 (as of 22 Sept 2026). Operators of critical facilities must meet the risk management duties of section 30 BSIG, the specific requirements of section 31 BSIG (including attack detection systems) and the evidence duty of section 39 BSIG, the successor of the former section 8a (3). Evidence is due every three years through audits, inspections or certifications.
The KRITIS umbrella act (KRITIS-Dachgesetz) adds physical resilience duties. The Bundestag passed it on 29 January 2026, the Bundesrat approved it on 6 March 2026, it was promulgated on 16 March 2026 and entered into force on 17 March 2026 (as of 22 Sept 2026). Grid operators additionally follow the Energy Industry Act and the IT security catalogues of the Federal Network Agency. Which of this applies to you is a question for your legal and data protection team; we cover the technical side. Read the basics on our NIS2 page and the service offer under Compliance & Regulations.
Typical assets we connect and secure
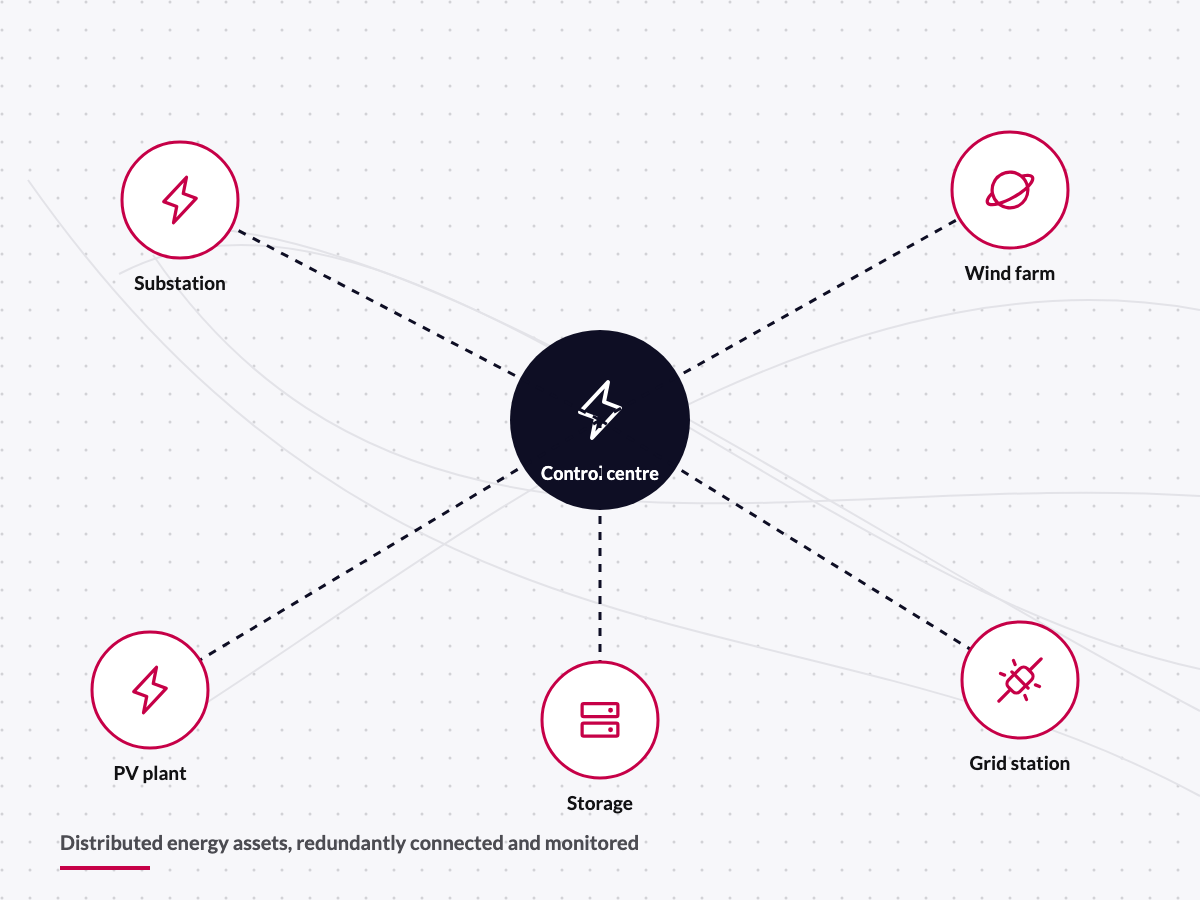
Energy infrastructure is distributed, mostly unmanned and runs on equipment that stays in the field for decades. Our approach is built for that.

Substations and secondary substations
Telecontrol (IEC 60870-5-104, IEC 61850) over LTE/5G with failover, the station network as its own zone, remote access only via a jump host.

Onshore and offshore wind farms
Connectivity for park controllers, SCADA and condition monitoring; offshore platforms and service vessels on Starlink or VSAT plus cellular.

Control rooms and grid control systems
Redundant WAN paths to the control centre, prioritised control traffic, separate zones for control, office and guest networks.

PV, biogas and storage sites
Many small sites, one standard build: routers, firewall rules and monitoring from a template, rolled out in series.

Gas and district heating plants
Connectivity for pressure regulation, metering and pumping stations, segmented process networks and documented hand-over points.

Construction and maintenance phases
Temporary connectivity for sites and commissioning, available as a rental if needed. See Rental.
What DRYNET delivers for critical infrastructure operators
Four building blocks that run stand-alone or as a managed service. We plan, install, document and operate, with technicians on site in northern Germany and beyond.

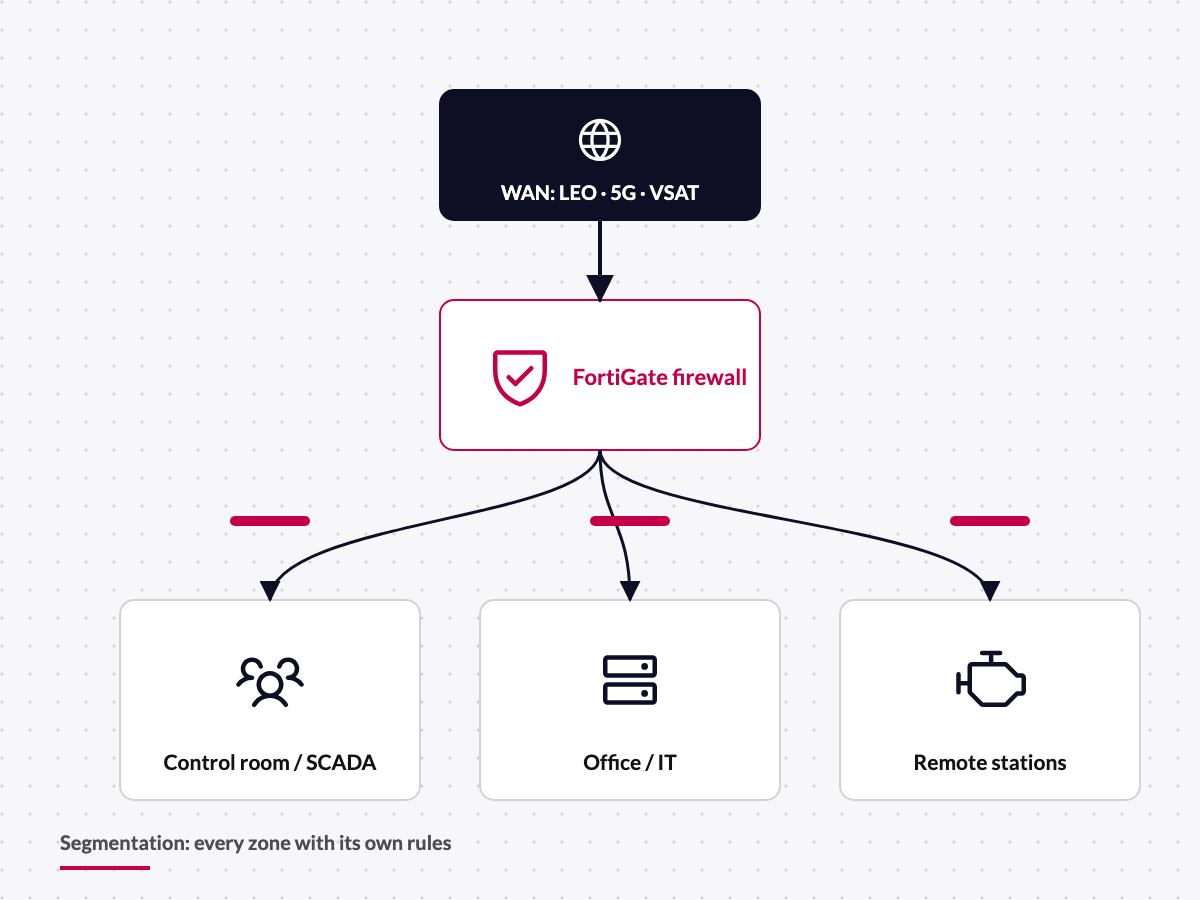
Segmented OT/IT networks to IEC 62443
We model zones and conduits, define the protection level per zone and implement the transitions with Fortinet firewalls. Existing plants usually migrate without an outage.

Hybrid connectivity for remote sites
LTE/5G as the primary link, Starlink or VSAT as backup, combined with Peplink SpeedFusion and hot failover. A site stays reachable even when one network goes down. IRIS², the EU constellation for secure connectivity with 348 satellites in LEO and MEO, is the coming European option; first launches are planned for 2029 (as of September 2026). We advise on it, see satellite communication.

Secure remote access for vendors and contractors
Time-limited, logged sessions with multi-factor authentication instead of permanent vendor tunnels. You can see who accessed which asset and when.

24/7 monitoring and audit documentation
Availability, link quality and security events converge in our monitoring. Network diagrams, rule sets and change history are delivered in a form you can use as evidence under section 39 BSIG.
How we work
No big bang. We work site by site and keep operations running.
Assessment
Asset inventory, existing remote access paths, WAN routes and responsibilities. We check which plants fall under BSI-KritisV or NIS2.
Target design and zone model
Zones, conduits and protection levels to IEC 62443, link mix per site, rule sets for firewalls and remote access. Agreed with your CISO and control engineers.
Pilot and rollout
One site as the reference, then series production: pre-configured routers and firewalls, installation by our technicians, acceptance with a protocol.
Operation and evidence
Monitoring, patch and change management, 24/7 support by agreement. Documentation is maintained continuously, not just before the audit.
Why a single link is not enough
Critical sites need paths that fail independently. We check these points in every design:
- Two physically separate transport paths (for example cellular plus satellite, or cellular from two carriers)
- Hot failover without session drops for telecontrol and voice traffic
- Prioritisation: control before cameras, cameras before office traffic
- Encrypted tunnels to the control centre, independent of the transport network
- Autonomous power supply for the network equipment for the duration of an outage
- An alarm when a backup link fails silently, not only when both are gone
Frequently asked questions about critical infrastructure and energy networks
We are below the KRITIS thresholds. Does this still concern us?
Very likely. NIS2 is tied to company size and sector, not to thresholds. Energy companies with 50 or more employees, or above EUR 10 million in turnover and balance sheet, are usually "important entities" and must register and implement risk management measures. Your legal team makes the formal classification.
What does IEC 62443 mean in practice for our substation network?
The standard groups systems into zones with the same protection requirements and controls the transitions between them (conduits). For a substation that usually means control, protection, cameras and service access are separate zones, and every transition passes a firewall with documented rules. We implement this with Fortinet components and deliver the zone model as a document.
Can we use Starlink for critical sites?
As a backup link, yes; as the only path, no. Starlink Business offers Priority plans with defined data blocks; for fixed sites within Germany that is "Local Priority" (as of 22 Sept 2026). We combine the satellite link with cellular and merge both via SpeedFusion, so control traffic runs encrypted and with failover. We source Starlink hardware and plans through our partner Tototheo and integrate them into your network; DRYNET is not a Starlink reseller.
How does secure remote access for equipment vendors work?
Through a central access platform: the vendor signs in with multi-factor authentication, gets access only to the released zone and only for the agreed period. Every session is logged. Permanent vendor routers inside the station network are replaced in the process. More under Secure Remote Access.
What documentation do we need for the evidence under section 39 BSIG?
Auditors want to see that measures are implemented and maintained: network diagrams with zones, firewall rule sets with justification, a list of remote access paths, monitoring reports, change history and patch levels. We hand over these documents in a structured form and keep them current during operation.
Does segmentation require an outage?
Usually not. We build the new structure in parallel, move systems zone by zone during maintenance windows and only remove old paths once the new path has proven itself.
Do you offer attack detection systems?
We integrate the detection functions of the deployed firewalls and our monitoring into your existing SIEM, or forward events to your provider. A complete attack detection system under section 31 BSIG is planned together with you and suitable partners; we do not promise what we do not operate ourselves.
Discuss your project
Prefer to talk? +49 431 55607040
Related services
Critical infrastructure & energy
Networks that stand up to an audit
From assessment to 24/7 operation: DRYNET plans, builds and runs your plant networks.