 Peplink Gold Partner
Why Fortinet when network and security belong together
Fortinet builds firewalls, switches, access points and endpoint agents on one operating system: FortiOS. Fortinet calls this combination the Security Fabric: an architecture that links endpoints, network and cloud through central analysis and automates the response. According to Fortinet, FortiGate is the most deployed network firewall with over 50 percent global market share (as of September 2026).
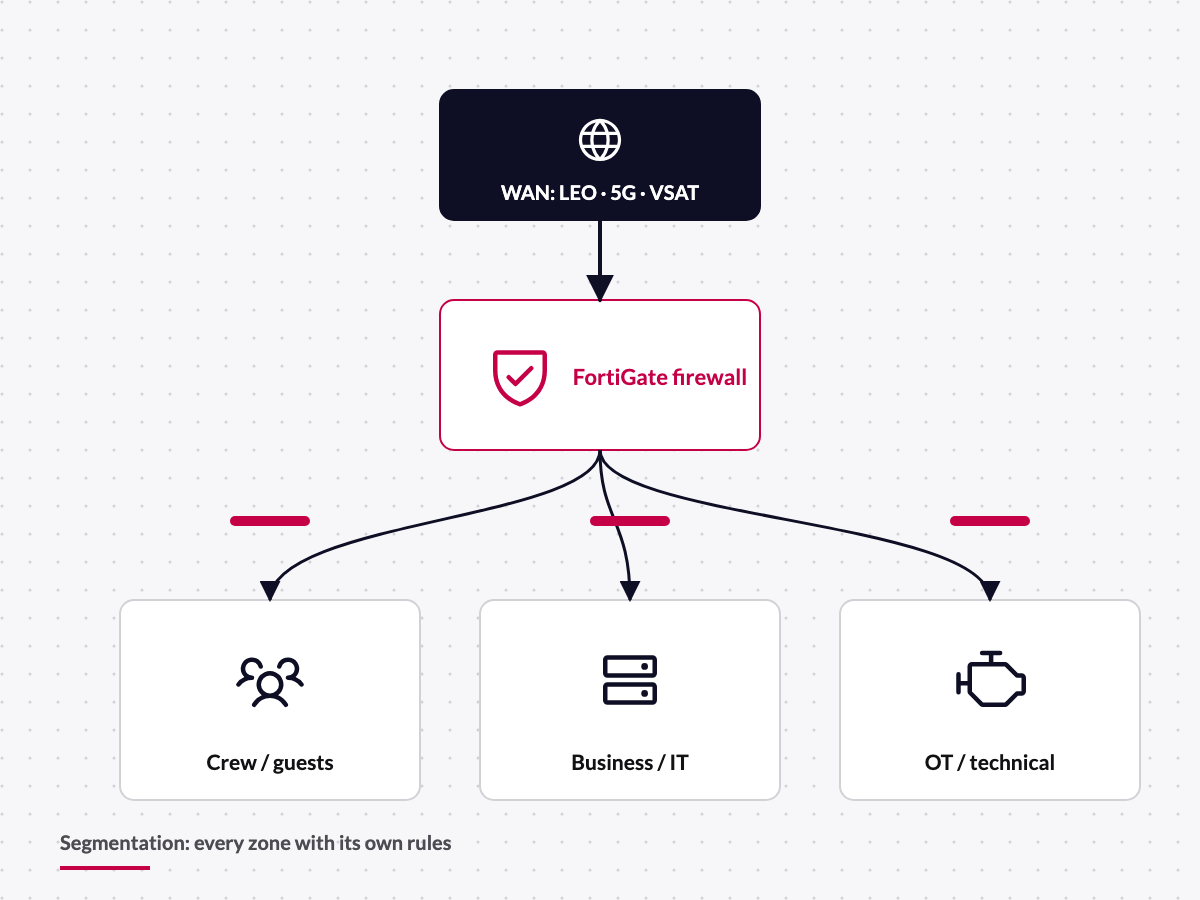
For us the practical side counts: a FortiGate is firewall, router, VPN gateway, wireless and switch controller in one device. Separating crew, business and OT networks becomes configuration, not cabling. What Fortinet does not deliver, we do: design, rule sets, migration and operation from Kiel.
- One operating system for firewall, switching, Wi-Fi and remote access
- Rugged models for vessels, cabinets and outdoor sites
- Central logging and management as NIS2 and audit evidence
- Engage Partner: sales, installation and operation from one source
Fortinet product families DRYNET works with
The building blocks from our projects; model and licence scope are set in the design.

FortiGate NGFW and FortiGate Rugged
Next-generation firewalls from compact models for vessels and branches to campus appliances. The Rugged series (as of September 2026: models 50G to 70G, some with one or two 5G modems) is fan-less and built for heat, cold, vibration and interference.

FortiSwitch and FortiAP
Switches and access points that extend the FortiGate via FortiLink. According to Fortinet, NAC is included without additional licensing; the FortiGate controls segmentation down to the port. Rugged switches and outdoor APs for deck, quay and cabinet.

FortiAnalyzer and FortiManager
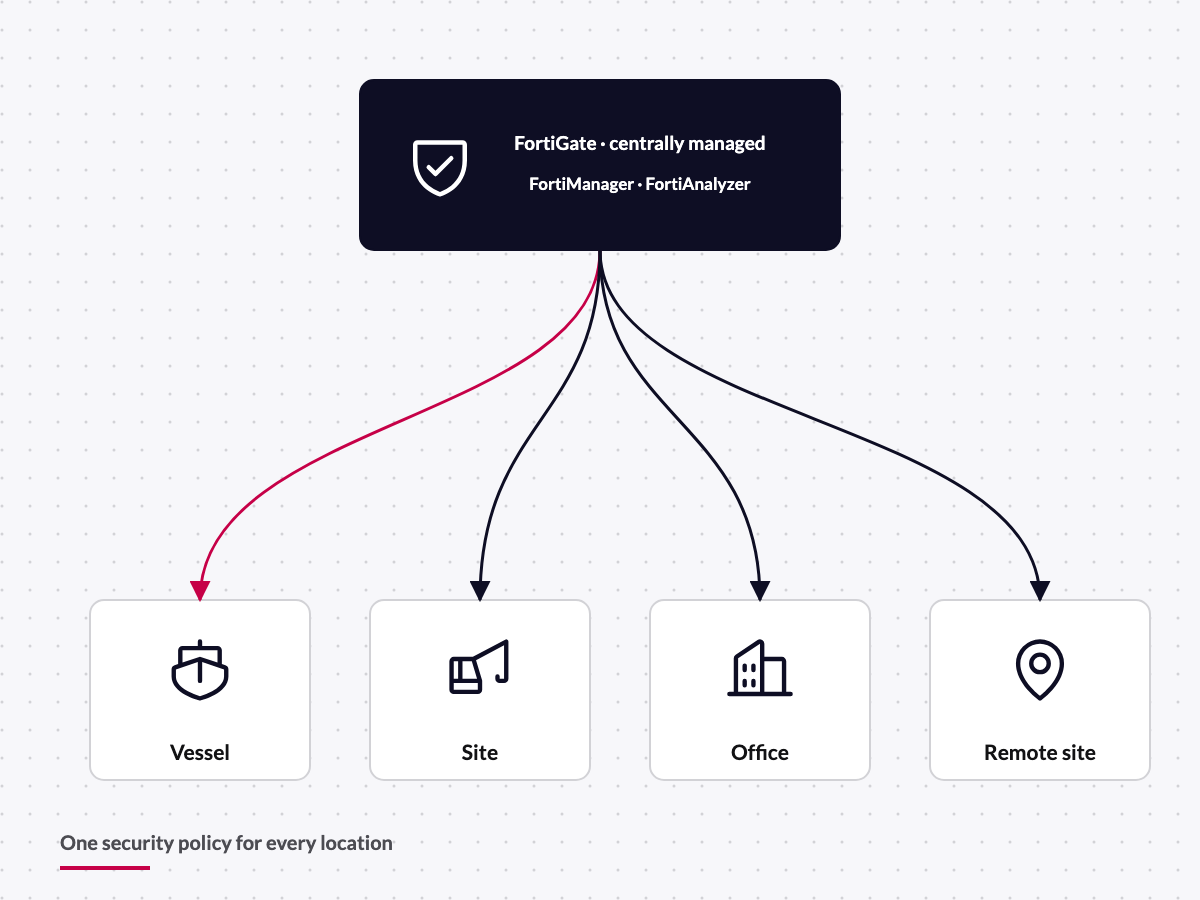
FortiAnalyzer collects logs from all components and produces audit reports. FortiManager pushes policies and firmware centrally – the basis for identical configurations across a fleet.

FortiClient and ZTNA
One agent for VPN, Universal ZTNA and endpoint protection, managed through FortiClient EMS. Remote maintenance runs per application and only from verified devices.
Where we deploy Fortinet
Four environments, one rule: what need not talk cannot see each other.

Vessel and fleet
Crew Wi-Fi, business network and bridge or engine systems as separate zones behind a compact FortiGate. Remote maintenance via ZTNA instead of open ports.

Critical infrastructure and utilities
Zones and conduits per IEC 62443: FortiGate Rugged between control system, field level and telecontrol. More under Critical infrastructure & energy.

Port and terminal
Cameras, access systems, crane control and guest Wi-Fi on one infrastructure, separated via FortiSwitch, FortiAP and FortiLink.

Office site with SD-WAN
FortiGate as firewall and Secure SD-WAN gateway for sites with two lines, managed through FortiManager.
Fortinet Secure SD-WAN or Peplink SpeedFusion?
Both are SD-WAN, and we use both. Fortinet Secure SD-WAN is built into FortiOS: the FortiGate steers applications across the available lines, inspects locally and is orchestrated through FortiManager. That suits offices, data centres and utilities with fixed lines.
Peplink SpeedFusion specialises in mobile links: cellular, Starlink and VSAT are bonded and sessions survive a link change – our first choice on vessels and construction sites. Often we combine both: Peplink bonds, the FortiGate behind it segments, filters and logs. See Peplink and SD-WAN Gateway.
What DRYNET adds beyond the manufacturer
Ordering a FortiGate is quick. A rule set that holds up in an audit is work – ours.

Design and segmentation
Survey systems, define zones for crew, business, OT and guests, choose model, licence bundle and redundancy.

Rule set and documentation
Least-privilege policies, named, commented and documented.

Migration of existing firewalls
Translate rule sets from other vendors, build the FortiGate in parallel, cut over in a maintenance window.

Managed firewall and 24/7
Changes, firmware, log review and incident handling around the clock: Managed Services.

Licences and FortiCare
FortiGuard bundles (ATP, UTP, ENT) and FortiCare levels (Essential, Premium, Elite) renewed in time, RMA handled with Fortinet.

Training and handover
Your IT team or onboard electricians learn the interface, daily tasks and escalation path.
Fortinet and NIS2: measures under § 30 BSIG
Section 30(2) BSIG lists ten areas of measures. A Fortinet environment provides the technical foundation for several; the concept remains yours. More under NIS2.
- Access control (no. 9): segmentation, roles and ZTNA policies on FortiGate and FortiClient EMS
- Cryptography (no. 8): IPsec and SSL VPN, encrypted remote maintenance
- Multi-factor authentication (no. 10): MFA for administrators and remote access
- Incident handling (no. 2): IPS and FortiGuard detection, central logs and alerts in FortiAnalyzer
- Business continuity (no. 3): configuration backups in FortiManager, HA pairs at critical boundaries
- Effectiveness assessment (no. 6): FortiAnalyzer reports as audit evidence
What Engage Partner means
Fortinet organises its partners in the Engage Partner Program, built on three pillars according to the manufacturer: engagement level, business model (integrator, MSSP or marketplace) and optional specialisations such as SD-WAN or operational technology.
DRYNET is a certified Engage Partner and authorised to sell Fortinet products. Hardware, licences, installation and operation come from one source; RMA cases go directly to Fortinet. Prices on request: model, licence bundle and term set the final price. All manufacturers: Technology partners & brands.
Frequently asked questions about Fortinet
Which FortiGate suits a vessel?
Usually a compact entry-level model, or a FortiGate Rugged in the engine room or an unventilated cabinet. Zones, WAN throughput and whether VPN, wireless and switch controller share one device decide.
Can you replace our firewall from another vendor?
Yes. We export the rule set, clean it up and translate it to the FortiGate. The new firewall runs in parallel; the cut-over happens in a maintenance window.
Do I need FortiAnalyzer and FortiManager?
Not necessarily for one site. With several vessels or sites, NIS2 evidence duties or operation by us, we recommend both: FortiAnalyzer for logs and reports, FortiManager for consistent policies and firmware.
What is the difference between FortiCare and FortiGuard?
FortiCare is manufacturer support for hardware and FortiOS (Essential, Premium, Elite). FortiGuard covers security services such as IPS, antivirus and web filtering in the ATP, UTP and ENT bundles. A FortiGate needs both; we track the terms.
Fortinet or Peplink?
They complement each other. Peplink SpeedFusion bonds changing links such as 5G, Starlink and VSAT; the FortiGate behind it segments, filters and logs. At office sites with fixed lines the FortiGate alone is often enough.
Does Fortinet help with NIS2 implementation?
For the technical measures in § 30 BSIG – access control, cryptography, MFA, attack detection – yes. Risk analysis, training and supply chain remain your task. More under NIS2 and Compliance & Regulations.
Request a Fortinet project
Prefer to talk? +49 431 55607040
Related services
Fortinet Engage Partner Kiel
Let's talk about your firewall
Send us your site, vessel or project outline. We reply with a proposal for model, segmentation and operation.